Key Takeaways
- TAA-compliant mobile repair requires parts from TAA-designated countries and qualifying facilities, with non-compliance risking contract termination and False Claims Act exposure.
- Procurement officers verify parts origin, facility locations, security certifications and audit trails based on documentation, not vendor statements.
- TAA compliance aligns with NIST SP 800-88, CMMC and SOC 2 to meet federal security and data sanitization standards for mobile devices.
- Common procurement gaps include missing component-level checks, omitting TAA clauses in contracts and overlooking supply chain changes during performance.
- Premier Logitech delivers TAA-certified mobile repair with CAGE code 4WAJ9 and full compliance credentials, and agencies can request a compliance credential review for federal programs.
How TAA Rules Shape Mobile Repair Requirements
The Trade Agreements Act of 1979, codified at 19 U.S.C. § 2501 et seq. and implemented through FAR Subpart 25.4, limits federal purchases to products manufactured in the United States or in countries with qualifying trade agreements. For mobile repair services, TAA compliance covers the service, the components used and the facilities where repairs occur.
Under TAA rules, a product’s country of origin follows the substantial transformation test, where processing creates a new article with a distinct name, character or use. Assembly, repackaging or relabeling alone does not change a product’s origin. For mobile repair, replacement parts must be wholly manufactured or substantially transformed in the United States or a TAA-designated country. Parts from non-designated countries such as China, India, Malaysia or Vietnam can render an entire repair non-compliant.
TAA-designated countries fall into four categories under FAR 25.003: WTO Government Procurement Agreement parties, Free Trade Agreement partners, Caribbean Basin countries and Least Developed Countries, totaling roughly 120 to 140 countries. These include the United States, Mexico under USMCA, Canada, EU member states, Japan, South Korea, Taiwan, Singapore, Israel and Australia.
TAA compliance applies to GSA MAS contracts at the contract level. A $5,000 GSA Schedule order still falls under TAA because the contract value exceeds the threshold. The current WTO GPA threshold for supply contracts is $174,000, effective March 13, 2026, under FAR Case 2025-007.
Core Requirements for TAA-Compliant Mobile Repair Vendors
Procurement officers evaluating mobile repair vendors for federal work confirm that vendors meet these core requirements.
- Parts origin documentation: All replacement parts must come from TAA-designated countries. Vendors provide written documentation proving country of origin for every component, tied to specific part numbers instead of broad product-family claims.
- TAA-compliant facilities: Repair processes take place in facilities located in the United States or other TAA-designated countries. Vendors disclose facility locations and support independent verification.
- Security standards compliance: Vendors follow federal security requirements, including NIST SP 800-88 for data sanitization of devices with sensitive information. Vendors handling Controlled Unclassified Information may require CMMC certification.
- Comprehensive audit trails: Vendors maintain detailed, serial-number-level records of parts sourcing, repair processes and data destruction that support compliance audits. These records remain available under FAR record-keeping requirements.
- Relevant certifications: TAA credentials, ISO quality frameworks, SOC 2 and related certifications show a structured approach to compliance and security.
Premier Logitech satisfies these requirements with TAA credentials, CAGE code 4WAJ9, ISO quality frameworks, NIST alignment, CMMC and SOC 2 certifications.
Request a vendor qualification review to confirm Premier Logitech compliance credentials for federal programs.
Checklist to Confirm a Vendor’s TAA Compliance
Verifying TAA compliance relies on documented evidence instead of vendor assurances. Post-hoc vendor statements carry less weight than a pre-purchase paper trail. This checklist supports structured vendor evaluation.
Documentation verification:
- Start by requesting a written TAA certificate of compliance on company letterhead. The certificate specifies the exact services and parts covered.
- Then request country-of-origin documentation for all replacement parts, tied to specific part numbers, to support that certificate.
- Review the vendor’s supplier list and confirm that each supplier operates in a TAA-designated country.
- Confirm the vendor follows a documented process that keeps parts sourcing limited to TAA-designated countries.
Facility and process verification:
- Schedule site visits or third-party audits of repair facilities to validate claims.
- Confirm that repair facilities operate in the United States or other TAA-designated countries.
- Compare data security and sanitization procedures with NIST SP 800-88 requirements.
- Check that audit trail practices align with FAR record retention standards.
Reference and track record checks:
- Request references from other federal agencies or defense contractors that used the vendor.
- Review the vendor’s GSA Schedule status and performance history.
- Verify CAGE code and SAM.gov registration status.
- Review past compliance findings or audit results for patterns.
Ongoing compliance monitoring:
- Set clear requirements for vendor notification of any supply chain changes.
- Plan periodic compliance reviews or audits during contract performance.
- Require updated certifications each year or whenever parts sourcing changes.
Integrating TAA Compliance with NIST, CMMC and SOC 2
TAA compliance operates alongside other security frameworks. Federal mobile repair programs align TAA requirements with NIST, CMMC and SOC 2 controls.
Programs start with NIST SP 800-88 for media sanitization. This standard defines three sanitization methods, Clear, Purge and Destroy, for rendering data unrecoverable. Mobile devices with sensitive information require Purge-level sanitization, such as cryptographic erase, or physical destruction before release. Vendors document sanitization processes and maintain certificates of destruction.
Where devices hold Controlled Unclassified Information, CMMC 2.0 for CUI handling adds another layer. Defense contractors handling CUI obtain CMMC certification. Practice MP.L2-3.8.3 requires sanitization or destruction of media with CUI before disposal or reuse. Mobile repair vendors supporting DoD contracts either hold CMMC certification or operate under a prime contractor’s approved plan. As of August 2026, Phase 1 self-assessment requirements apply under DFARS 252.204-7012, and Phase 2 C3PAO certification requirements remain under review.
SOC 2 for data security strengthens this posture. SOC 2 certification shows that a vendor manages data security, availability and confidentiality in a structured way, which matters for repair facilities handling government devices.
Programs turn these frameworks into a single process through a few integration steps.
- First align all repair and sanitization processes with NIST SP 800-88 guidelines to create a baseline.
- Next confirm that subcontractors handling CUI hold CMMC certification or fall under an approved plan, so the chain of custody stays protected.
- Throughout the lifecycle, maintain serialized logs of all devices sanitized or destroyed to support audits.
- Document third-party vendor practices when destruction vendors participate in the process.
- Store all compliance evidence in the System Security Plan, so reviewers can trace each control.
A single documented NIST SP 800-88 destruction process can satisfy CMMC, FISMA contractor and NISPOM requirements at once. Premier Logitech supports this alignment with documented compliance across ISO, NIST, CMMC and SOC 2 standards.
Procurement Steps for Federal Agencies
Federal teams follow a structured sequence to procure TAA-compliant mobile repair services.
- Identify the need and draft the RFP. Define the scope of repair services and include explicit TAA compliance clauses. Sample RFP language: “All repair services must be TAA compliant, with parts sourced from TAA-designated countries. Vendor must provide documentation proving country of origin for all replacement parts.”
- Use appropriate procurement vehicles. GSA MAS contracts and other approved vehicles require TAA compliance. Confirm that the solicitation includes FAR 52.225-5 (Trade Agreements) or the applicable TAA clause.
- Evaluate vendor proposals against TAA and security criteria. Apply the verification checklist to assess each vendor’s compliance documentation, facility locations, security certifications and audit trail capabilities.
- Award the contract and set ongoing monitoring. Include requirements for periodic compliance reviews, supply chain change notifications and updated certifications.
Schedule a procurement planning consult to structure TAA requirements into upcoming mobile repair RFPs.
High-Risk TAA Mistakes in Mobile Repair Programs
Pitfall 1: Assuming repair services meet TAA by default. Many vendors claim compliance without full understanding. Procurement teams verify documentation and conduct due diligence regardless of claims.
Pitfall 2: Skipping component-level origin checks. Vendors may source parts from non-designated countries without clear disclosure. Item-level verification functions as a key safeguard because manufacturers often report origin inconsistently. Contracts require part-level country-of-origin documentation and supplier list audits.
Pitfall 3: Treating TAA as a substitute for data security. TAA status does not address data handling. Programs confirm NIST SP 800-88 compliance and CMMC certification where CUI enters the scope.
Pitfall 4: Leaving TAA language out of contracts. Contracts that lack explicit TAA requirements expose agencies to risk. Teams reuse the sample RFP language and confirm that FAR clauses appear in final awards.
Pitfall 5: Relying on verbal assurances. A vendor’s verbal assurance after the fact is not a compliance record. Teams collect the paper trail before any purchase order and keep it ready for audit.
Pitfall 6: Overlooking mid-contract supply chain changes. If a product on a GSA Schedule becomes non-compliant because a manufacturer moved final assembly to a non-designated country, the contractor promptly submits a deletion modification. Continuing to sell a non-TAA product creates contract breach and False Claims Act exposure. Contracts include supply chain change notification requirements for every vendor.
Why Premier Logitech Fits Federal TAA Mobile Repair Needs
Premier Logitech aligns operations, facilities and certifications with the verification steps described above, which supports federal audit readiness.
- TAA credentials and CAGE code 4WAJ9: Status suited for U.S. federal government work.
- More than 20 OEM Authorized Service Centers: Authorized repair network for major device brands.
- Scalable depot repair operations: High-volume repair capacity that supports large federal programs.
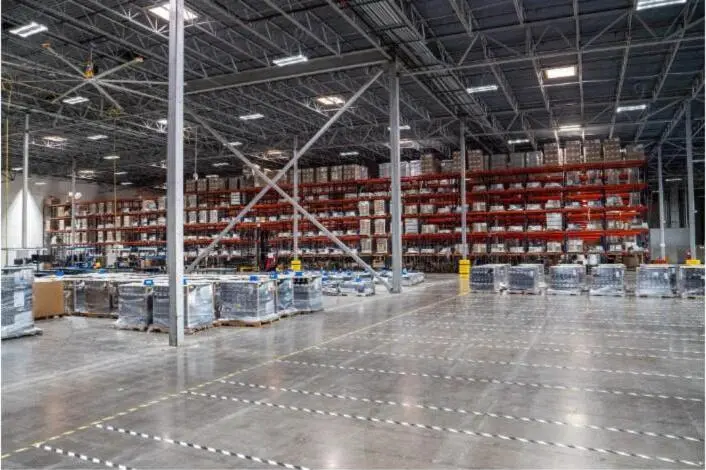
- Facilities in TAA-designated countries: U.S. operations in DFW and nearshore facilities in Mexico at Laredo and Nuevo Laredo, and Mexico qualifies under USMCA.
- Structured compliance program: As noted earlier, Premier Logitech holds the required TAA, ISO, NIST, CMMC and SOC 2 credentials.
- End-to-end lifecycle services: Sourcing through recycling, including NIST-aligned mobile device repair and SOC 2-certified repair operations.
These capabilities give procurement teams a verifiable evidence trail at the part, facility and process level, which supports OIG reviews and internal audits.
Connect with a federal lifecycle specialist to align Premier Logitech services with specific TAA-compliant mobile repair needs.
Frequently Asked Questions
What is TAA compliance for mobile repair?
TAA compliance for mobile repair means all replacement parts come from TAA-designated countries and repair services occur in facilities that meet Trade Agreements Act requirements under FAR Subpart 25.4. Compliance follows the substantial transformation test, which focuses on where a product was manufactured or fundamentally changed into a new article of commerce. Assembly or labeling alone does not control origin. For federal agencies, TAA compliance applies to GSA Schedule contracts and most procurements above the applicable dollar threshold, including the $174,000 figure noted earlier.
How do procurement officers verify a repair vendor’s TAA compliance?
Verification relies on written documentation instead of verbal assurances. Procurement officers request a TAA certificate of compliance on company letterhead that specifies the exact services and part numbers covered, country-of-origin documentation tied to specific components and evidence of facility locations in TAA-designated countries. Site visits or third-party audits, CAGE code and SAM.gov checks and references from other federal agencies form part of standard verification. Teams collect documentation before issuing purchase orders and retain it for the contract term and at least three years after performance under FAR record retention rules.
What documentation is required for TAA compliance audits?
Vendors maintain certificates of origin, supplier certifications, serialized audit trails linking each part number to its country-of-origin declaration, data sanitization records and destruction certificates. Documentation ties to the exact procurement record instead of broad product-family claims. For programs involving Controlled Unclassified Information, records also include NIST SP 800-88-compliant sanitization logs and, where applicable, evidence of CMMC certification or coverage under a prime contractor’s approved plan. All records stay available under FAR requirements and support OIG audit review.
Can TAA compliance be combined with NIST and CMMC requirements?
TAA compliance, NIST SP 800-88 data sanitization and CMMC certification operate together on many federal mobile repair contracts. A single documented NIST SP 800-88 destruction process can satisfy CMMC Practice MP.L2-3.8.3, FISMA contractor requirements and NISPOM at once. Procurement officers align all repair and sanitization processes with NIST SP 800-88, confirm that subcontractors handling CUI hold CMMC certification or fall under an approved plan and retain all compliance evidence in the System Security Plan. TAA compliance governs parts origin and facility location, while NIST and CMMC govern data security and sanitization, so programs address both areas in parallel.
What are the risks of using a non-TAA-compliant mobile repair vendor?
Risks include contract termination for default, False Claims Act liability with treble damages and civil penalties ranging from $14,308 to $28,619 per false claim under 31 U.S.C. § 3729, suspension or debarment from future federal work and supply chain security vulnerabilities from parts sourced in non-designated countries. Prime contractors carry full legal responsibility for TAA compliance of all products delivered under their contracts, including those sourced from subcontractors. A subcontractor’s failure to provide accurate origin data does not shift that liability. GSA’s Office of Inspector General regularly audits IT procurement for TAA documentation, and programs without strong certification trails face remediation.
